FALL//2026 Conference

November 5-6
150 Elgin Street, Suite 1800, Ottawa 🇨🇦

CONFERENCE SCHEDULE

COUNTERMEASURE Fall 2026 Conference

November 5-6, 2026
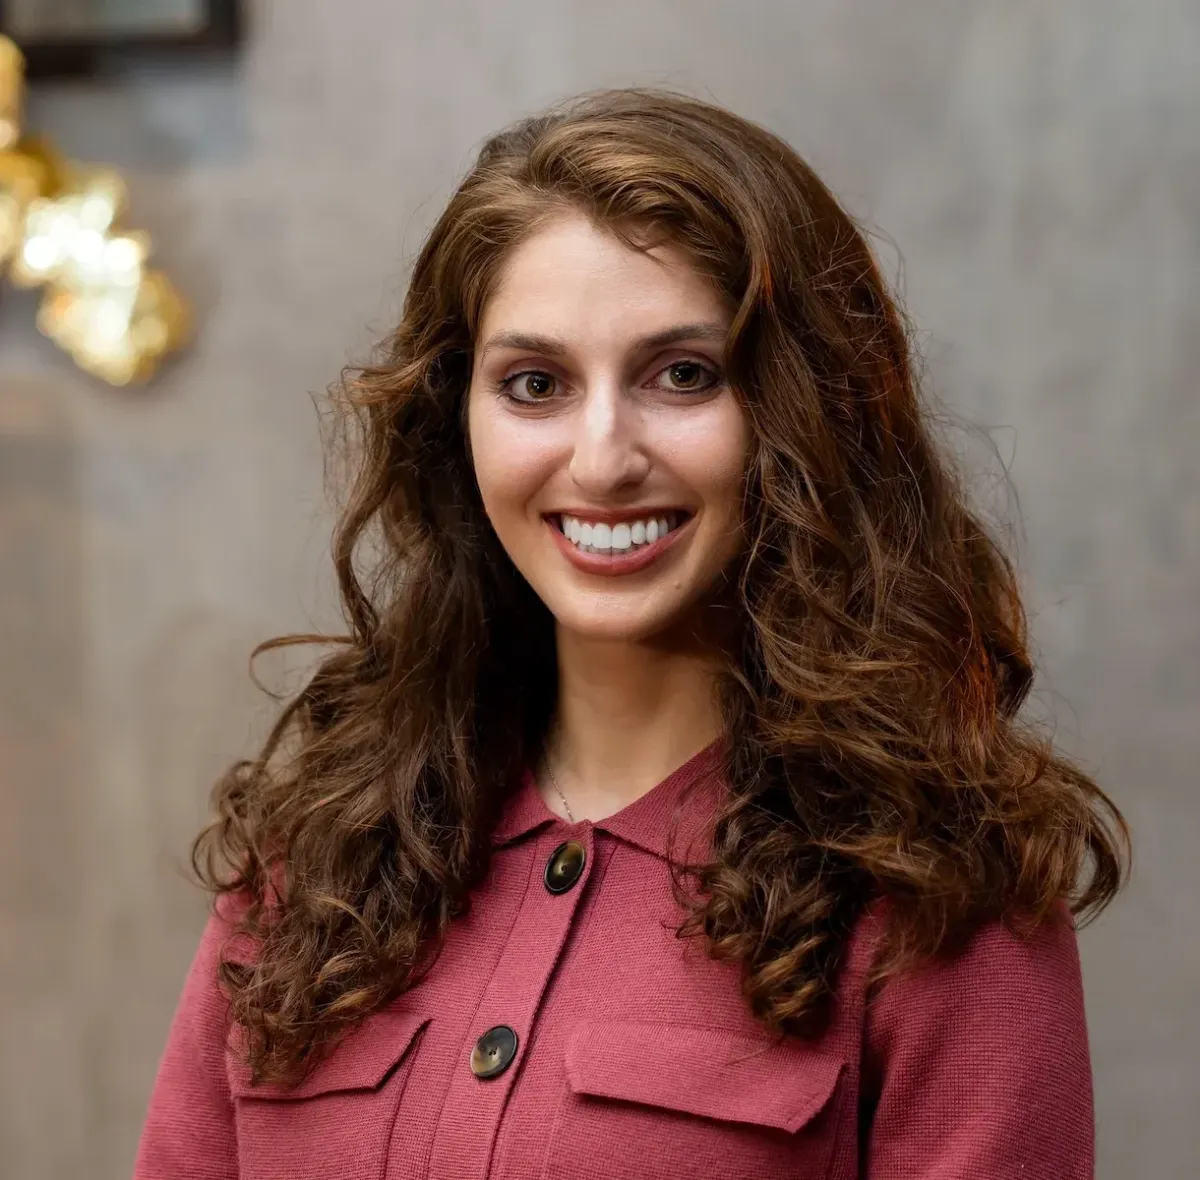
KEYNOTE // Daria Bahrami, Dreadnode
AI is accelerating cyberattacks while recovery remains slow, making the costs of conflict harder to contain. Drawing on SEC filings and attacks on hospitals and suppliers, this keynote examines recovery, economic fallout, and the erosion of the boundary between cybercrime and warfare.

KEYNOTE: Daria Bahrami, Dreadnode

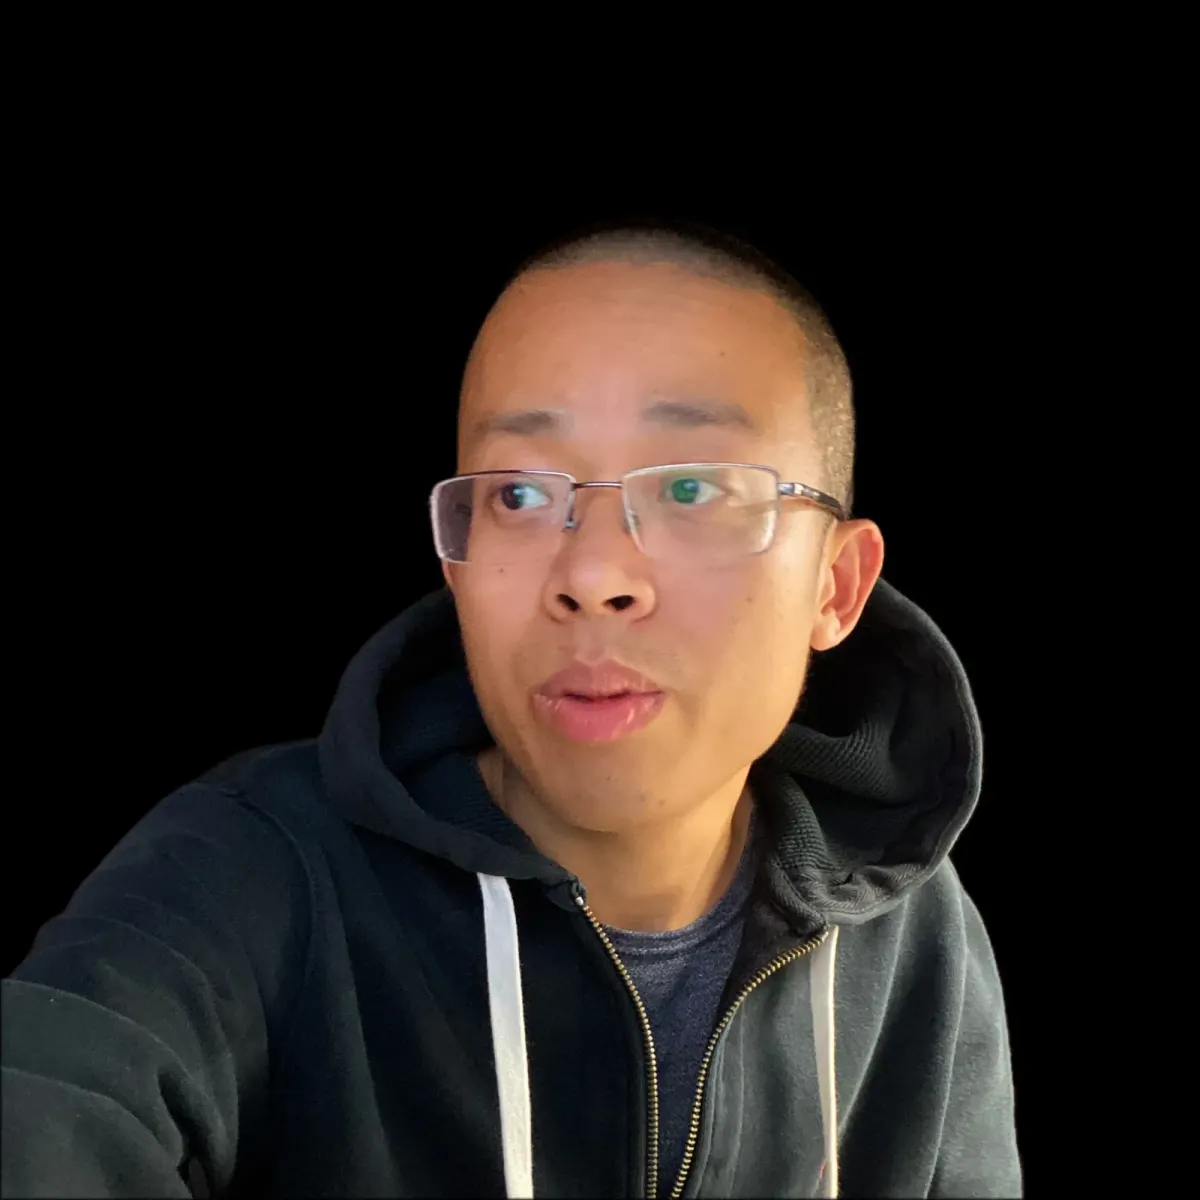
KEYNOTE // Bruce Dang, Calif.io
AI’s capabilities in bug discovery, exploitation, and reverse engineering have made Linux kernel exploits cost < $20, and OpenBSD exploits no longer rare. This keynote discusses applying frontier models to computer security problems, successes and failures, future challenges and preparations.

KEYNOTE: Bruce Dang, Calif.io

TALK: ZeroDay to Zero Dollars: Exploiting the Windows Management Instrumentation Device
This talk is the story of hunting for a zero day Windows Local Privilege Escalation (LPE) destined for a hacking competition, successfully weaponizing it, and then watching the payout evaporate entirely due to unlucky timing and an inconvenient patch.

SPEAKER: Erik Egsgard, Field Effect

TALK: Understanding ORBs, proxies and geospatial data exfiltration
This session examines proxy and relay infrastructure used to collect and exfiltrate geospatial data, covering its design, purpose, daily operations, national security implications, network observations, and potential attribution of backend interfaces.

SPEAKER: Dr. Fyodor Yarochkin, Trend AI
TALK: Beyond Autonomous Cyber: From Autonomous Silos to Mission Assurance at Machine Speed
Cybersecurity’s autonomous capabilities often operate in silos. Introducing Autonomous Mission Assurance: a human-governed architecture connecting development, operations, validation, compliance, remediation, and monitoring through shared context, evidence, orchestration, and bounded autonomy.

SPEAKER: Hahna Kane Latonick, Dark Wolf
TALK: The Edge Is Burning
Examines perimeter device compromises through a real-world edge appliance intrusion, showing how attacker tactics have evolved, why these cases are hard to investigate, and how defenders can improve visibility, readiness, and response.

SPEAKER: Matthew Graves, CSE

TALK: Break it, Catch it, Harden it: AI Agents Running a Full-Cycle Detection Pipeline
CCCS presents an LLM-driven purple-team pipeline that automates detection engineering, adversarial testing, telemetry validation, hardening, and triage. The talk examines architecture, failure modes, and which capabilities genuinely improved analyst effectiveness.

SPEAKER: Benoit Denis, CSE, Ayesha Bashir, CSE
TALK: What Still Works: Malware Analysis in the Age of Agents
This talk explores AI’s benefits and pitfalls in malware analysis, emphasizing the role of domain expertise. Using LegionLoader as a case study, it covers agent-assisted unpacking, C2 analysis, and extraction of cryptographic keys and indicators.

SPEAKER: Pierre-Marc Bureau

TALK: What are you Token' about?
Explore how Windows access tokens govern permissions, follow processes and threads, and enable impersonation. Learn how attackers abuse tokens to escalate privileges—and what defenders can monitor to spot misuse.

SPEAKER: Pavel Yosifovich

TALK: A "Fishy" Conference in Autumn
This talk traces an unusual surveillance operation tied to a real-world event, combining infrastructure analysis, OSINT, and on-the-ground context to reveal a novel commercial-spyware infection vector and explore its implications for espionage, attribution, and the future of surveillance.

[🔴 TLP:RED] SPEAKER: Julian-Ferdinand Vögele, Recorded Future
TALK: Under the wire - detecting targeted attacks against government networks with JA4 and X509 chain validation
A case study of forged X.509 certificates used to intercept logins to Cisco SSL VPNs at U.S. government networks. Learn how the technique connects to proxy infrastructure and how JA4 fingerprinting can help defenders detect and disrupt similar attacks.

[🔴 TLP:RED] SPEAKER: Christy Jay Quinn, Infrawatch
TALK: Reasoning Models // Non-Reasoning Humans
Military AI can aid high-stakes decisions, but visible reasoning may not reflect how newer models reach conclusions. This talk examines the resulting trust gap and explores alternatives to chain-of-thought for meaningful human oversight.

SPEAKER: Mauro Vignati, ICRC

TALK: Studying the PRC Vulnerability Research Ecosystem with AI-Enabled Open-Source Social Network Graphs
This talk examines how AI can build and analyze social graphs of adversarial networks, using China’s vulnerability research ecosystem as a case study. It explores how incomplete or leak-skewed data can distort graph algorithms—and how analysts can mitigate these pitfalls.

[🔴 TLP:RED] SPEAKER: Ian Roos, Amelia Shapiro, Phyle
PANEL: Faster Than Our Guardrails - AI on Offence, Defence, and Everything in Between
Experts in AI-enabled cyber offense and defense examine real shifts in exploit development and malware, separate credible risks from hype, and explore how organizations can govern and control increasingly capable AI agents.

PANEL DISCUSSION led by Matt Holland, CEO, Field Effect
PANELIST
PANELIST: Faster Than Our Guardrails - AI on Offence, Defence and Everything in Between

PANELIST: Po Tea-Duncan, GC CISO, Treasury Board of Canada Secretariat
LIGHTNING TALK
Lightning Talk Speaker

LIGHTNING TALK: Joey Dube, CCCS

LIGHTNING TALK
Lightning Talk Speaker

LIGHTNING TALK: Paul Belanger, CSE

LIGHTNING TALK
Lightning Talk Speaker

LIGHTNING TALK: Guillaume Lacasse, CSE

Conference Schedule

Time DAY 1 - November 5
8:30-9:30 KEYNOTE // At the Edge: The Rising Cost
of Our Cyber Pain Threshold

by Daria Bahrami, Dreadnode
9:30-10:15 Reasoning Models, Non-Reasoning Humans
by Mauro Vignati, ICRC
10:15-10:30 BREAK
10:30-11:15 Studying the PRC Vulnerability Research
Ecosystem with AI-Enabled Open-Source
Social Network Graphs

by Ian Roos and Amelia Shapiro, Phyle
11:15-12:00 Understanding ORBs, proxies
and geospatial data exfiltration

by Dr. Fyodor Yarochkin, Trend AI
12:00-13:00 LUNCH
13:00-13:45 The Edge is Burning
by Matt Graves, CSE
13:45-14:30 Under the wire:
Detecting targeted attacks
against government networks
with JA4 and X509 chain validation

by Christy Jay Quinn, Infrawatch
14:30-14:45 BREAK
14:45-15:30 A "Fishy" Conference in Autumn
by Julian-Ferdinand Vögele, Recorded Future
15:30-16:15 Lightning Talks and Day 1 Closing Remarks
16:30-19:00 COUNTERMEASURE Networking Reception
Time DAY 2 - November 6
8:30-9:30 KEYNOTE // Adapting to the
brave new world of computer security

by Bruce Dang, Calif.io
9:30-10:15 Beyond Autonomous Cyber:
From Autonomous Silos to Mission Assurance
at Machine Speed

by Hahna Latonick, Dark Wolf
10:15-10:30 BREAK
10:30-11:15 What Still Works: Malware Analysis
in the Age of Agents

by Pierre-Marc Bureau
11:15-12:00 ZeroDay to Zero Dollars:
Exploiting the Windows
Management Instrumentation Device

by Erik Egsgard, Field Effect
12:00-13:00 LUNCH
13:00-13:45 What are you Token' about?
by Pavel Yosifovich
13:45-14:30 Break it, Catch it, Harden it:
AI Agents Running a Full-Cycle
Detection Pipeline

by Benoit Denis and Ayesha Bashir, CSE
14:30-14:45 BREAK
14:45-15:45 Panel Discussion
by Matt Holland, Field Effect
15:45-16:15 Conference Closing Remarks and Prizes
16:30-19:00 Post Conference Reception

Registration Charges

Pricing
Model
Conference
Only
Early Bird
(Till Aug 7)
CAD 750
Standard
(Aug 8 - Sep 30)
CAD 850
Late
(Oct 1 - Oct 26)
CAD 950

Conference Venue

KPMG, 150 Elgin St, Suite 1800, Ottawa


Ringzer0 COUNTERMEASURE Advisory Board

Meet Our Advisors
SPRING 2026 // FALL 2026

COUNTERMEASURE FALL//2026 TRAINING

Our Sponsors

Great! Next, complete checkout for full access to Ringzer0
Welcome back! You've successfully signed in
You've successfully subscribed to Ringzer0
Success! Your account is fully activated, you now have access to all content
Success! Your billing info has been updated
Your billing was not updated